Follow
https://cyberpress.org/ta4922-hackers-use-tax-phishing/
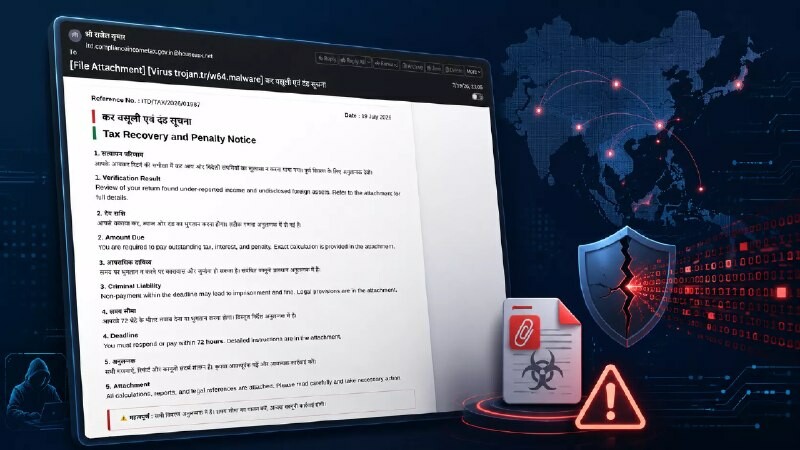
TA4922 Hackers Use Tax Phishing to Deploy PackClient RAT Across Asia TA4922 is identified as using tax-themed phishing to deliver the PackClient RAT across Asia. The activity links a Chinese-speaking threat actor to credential-style lures built around tax matters, with malware deployment centered on a modular remote access framework. Operationally