Follow
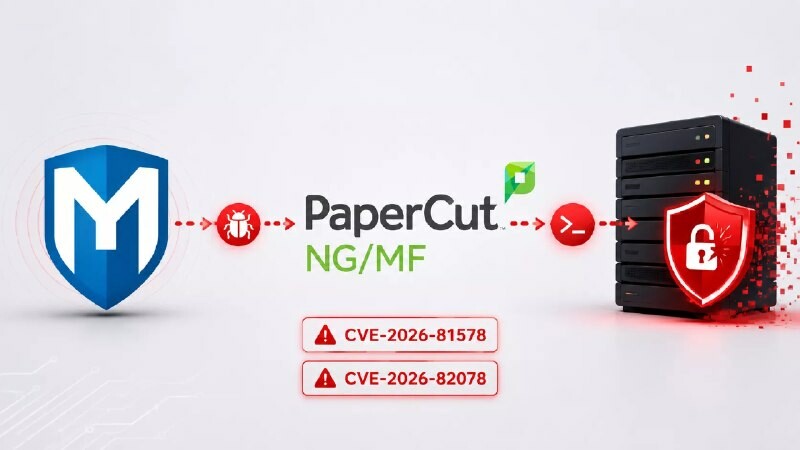
Metasploit Module Expands PaperCut Zero-Day Exposure A new Metasploit module targets an actively exploited PaperCut NG/MF RCE chain built from CVE-2026-81578 and CVE-2026-82078. The flaws pair authentication bypass with unsafe dynamic class loading, allowing unauthenticated code execution. PaperCut says all NG/MF versions may be affected, with Emergency Patch Release 2 issued for supported 24.x, 25.x, and 26.x branches.
https://cyberpress.org/metasploit-exploit-targets-actively-exploited/